Cybersecurity
Security for businesses that can't afford a breach.
Attackers don't pick targets by size — automated scanners sweep the whole internet for anything left open. I find what they'd find first, explain it in plain English, and close it.
Attack → defence
What I protect you from.
Every website and app I build ships with these in place. Already have a site? I can harden it.
Scammers emailing your customers as you
SPF, DKIM & DMARC on your domain so forged mail is rejected before it reaches an inbox.
Logins, forms and payments read in transit
HTTPS everywhere with modern TLS and HSTS, so no page can be quietly downgraded.
Malicious scripts injected into your pages
A strict Content Security Policy and hardened headers that stop injected code and clickjacking.
Customer sessions hijacked
Secure, HttpOnly, SameSite cookies — session tokens that can't be stolen by scripts or other sites.
Spam and bots flooding your forms
Server-side validation, rate limiting and abuse protection on every form and API.
Outdated software advertised to attackers
Version banners removed and dependencies kept patched, so scanners have nothing to match.
Free tool
Is your website leaving the door open?
Type in your domain and get a passive security check in seconds — HTTPS, headers, cookies and whether scammers can send email as you. Every finding explained in plain English, with the fix.
Scan my website freeNo sign-up. Passive checks only — nothing is attacked.
- HTTPS & TLS certificate[PASS]
- Security headers (CSP, HSTS…)[WARN]
- Cookie flags[PASS]
- Email spoofing (SPF / DMARC)[FAIL]
- Mixed content & version leaks[WARN]
Credentials
Trained on real attacks, in real labs.
Cybersecurity diploma coursework and hands-on labs — Kali Linux, Nessus, Nmap, Metasploit, OSINT — each documented as an evidence-based report. Working toward eJPT → OSCP.
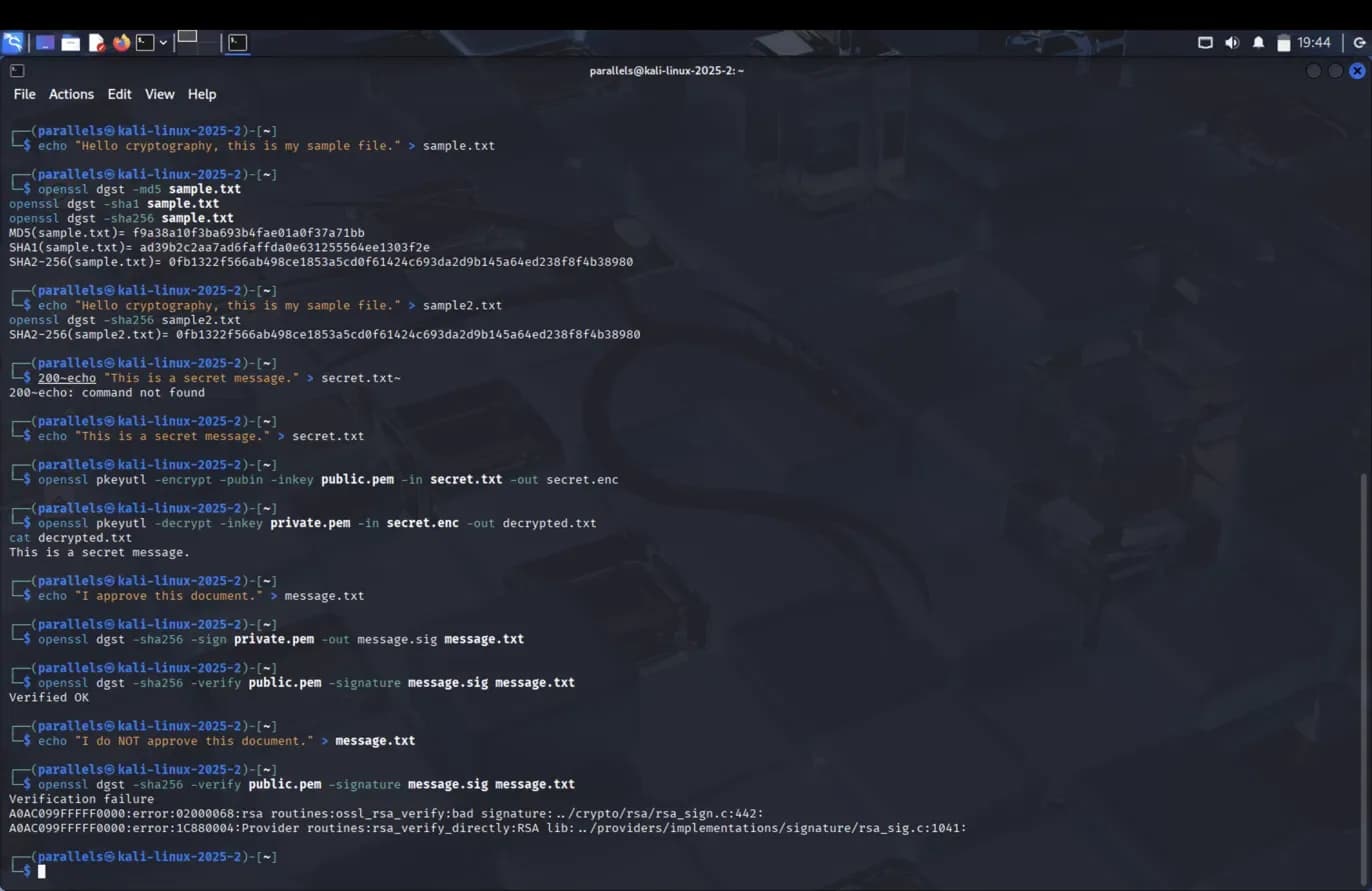
OpenSSL Cryptography Lab
hashing · RSA encryption · digital signatures
Lab write-ups
- Kali Linux
- Nmap
- Nessus
- Wireshark
- Burp Suite
- Metasploitable2
- OSINT Tools
Taking new projects
Close the gaps before someone finds them.
See exactly what you'd get and a fixed price in about a minute — free, no obligation. Or call me; you'll talk to the person who builds it.
+1 778-872-3597